Briefing
Ransomware penetration testing: could an intruder reach what you would need to recover?
Ransomware penetration testing focuses on one question leadership cares about most. If an intruder got in, could they reach the systems and backups you would need to recover? So the mandate tests reach and recovery, not encryption.
- Principal-led mandates
- Fixed fee agreed in writing
- Nothing retained afterwards
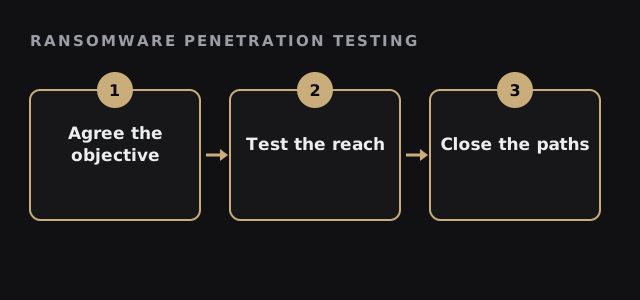
What ransomware penetration testing measures
No real ransomware is used, and nothing is encrypted. Instead, the mandate measures whether the conditions an attacker relies on are present.
- Whether a foothold could spread across the estate
- Whether backups are reachable from ordinary accounts
- Whether privileged access is segmented
- Whether detection would notice before it mattered
How ransomware penetration testing is scoped
The objective is written in business terms, for example reaching the backup console from a standard workstation. Therefore the report reads as a route, and leadership can see exactly where it breaks.
| Objective | Why it matters | Evidence returned |
|---|---|---|
| Reach the backups | Recovery depends on them. | The route, or proof it is closed. |
| Gain wide privilege | Spread needs it. | Each step and its fix. |
| Go unnoticed | Time is the attacker's ally. | What was and was not detected. |
Readiness for ransomware penetration testing
Tick what is true today. Gaps shape the objective.
Your result appears here as you tick, so you can see what is still open.
Safety during ransomware penetration testing
The rules of engagement exclude anything destructive, and backups are observed rather than altered. In addition, a stop procedure and named contacts are agreed first. Also, every artefact placed is removed at close.
What leadership receives
You receive the routes with evidence, a ranked plan and a debrief from the professional hacker who led the work. Because recovery planning sits with you, the findings map to the controls in the CISA #StopRansomware Guide. The retest is included.
Fees and fit
Full mandates run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Exposure Assessment starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. The fee is fixed after the written scoping brief, then invoiced against milestones.
Ransomware penetration testing questions
Does ransomware penetration testing use real ransomware?
No. Nothing is encrypted, and destructive actions are excluded in writing.
Can ransomware penetration testing touch our backups?
Backups are observed for reachability, never altered.
Is ransomware penetration testing the same as a tabletop exercise?
No. A tabletop rehearses the response, while this test checks real reach.
Who leads the mandate?
A senior professional hacker, personally, from scope to debrief.
Related guides
Request an introduction
Tell us which systems recovery depends on. A senior professional hacker replies within one business day when the mandate is a fit. Also, mention whether backups are held offline, because that usually decides the shape of the objective and its rules.
Request an introduction