Briefing
Enterprise penetration testing, led by one named principal
Enterprise penetration testing often fails for an organisational reason rather than a technical one. Large estates get large teams, so nobody holds the whole picture. A principal-led mandate solves that, because one senior person runs it end to end.
- Principal-led mandates
- Fixed fee agreed in writing
- Nothing retained afterwards
Where enterprise penetration testing goes wrong
Most large engagements split the estate between several juniors. As a result, routes that cross business units are missed, because each tester saw only a slice. Also, the person who writes the report often never touched the systems.
How principal-led enterprise penetration testing works
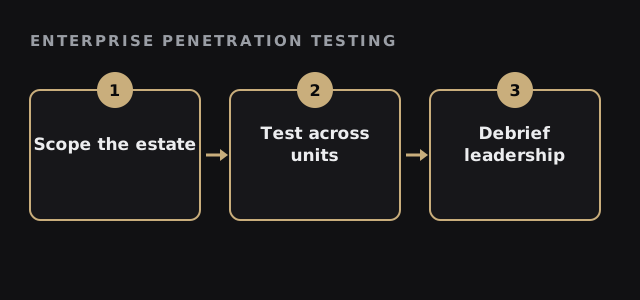
Here, one senior professional hacker scopes, runs and reports the mandate. Therefore the routes that cross teams, clouds and regions stay visible to one person.
| Typical large firm | Principal-led mandate | |
|---|---|---|
| Who tests | Whoever is free that month. | The named principal. |
| Who reports | Often a separate writer. | The person who tested. |
| Fee | Day rates, then change orders. | One fixed fee. |
Scope enterprise penetration testing
Tick what applies. More ticks usually mean a larger mandate.
Your result appears here as you tick, so you can see what is still open.
What enterprise penetration testing usually covers
Scope is agreed per business unit, then signed by each system owner.
- External perimeter across every region
- Internal estate, segmentation and directory services
- Cloud accounts and the trust between them
- Applications that carry the most business risk
Reporting to security leadership
The report is written for two readers. For example, engineers receive reproducible findings, while leadership receives risk in business terms and a ranked plan. In addition, the principal delivers the debrief personally, and the retest is included. The method follows the Penetration Testing Execution Standard.
Fees and capacity
Full mandates run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Exposure Assessment starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. Because capacity is the constraint, we accept a limited number of mandates each year.
Enterprise penetration testing questions
Can one person handle enterprise penetration testing?
One principal leads and holds the picture. The scope and timeline are sized to make that work.
How long does enterprise penetration testing take?
It depends on the estate. The fixed fee and milestones are agreed in the engagement letter.
Do you publish enterprise client names?
No. References are introduced in writing once the non-disclosure agreement is signed.
Is anything retained afterwards?
No. Evidence and findings are destroyed when the engagement closes.
Related guides
Request an introduction
Describe the estate and what leadership most wants answered. A senior professional hacker replies within one business day when the mandate is a fit. Also, include the regions and business units involved, because they shape the fixed fee and the timeline more than anything else.
Request an introduction