Briefing
Penetration testing in cyber security: what it proves, and what it does not
Penetration testing in cyber security is authorised attack simulation. So it proves what an intruder could actually reach, which no policy, audit or scanner can show on its own.
- Principal-led mandates
- Fixed fee agreed in writing
- Nothing retained afterwards
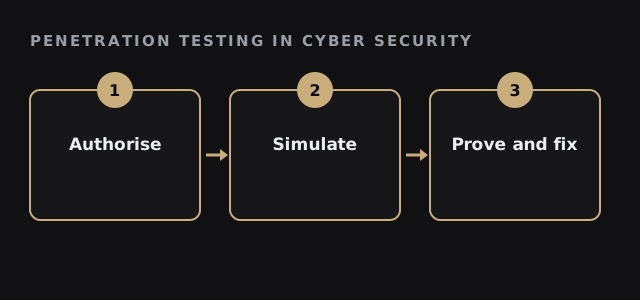
The role of penetration testing in cyber security
Most security work describes controls. By contrast, a penetration test challenges them. Therefore it answers a practical question for leadership: if someone tried, how far would they get?
Penetration testing in cyber security, beside other checks
Each activity answers a different question, so a mature programme uses all of them.
| Activity | The question it answers | What it misses |
|---|---|---|
| Vulnerability scan | What known issues exist? | Whether they connect. |
| Audit | Are the controls documented? | Whether they hold under pressure. |
| Penetration test | What could an intruder reach? | Anything outside the scope. |
Is your programme using penetration testing in cyber security well?
Tick what is already true. Gaps suggest where to start.
Your result appears here as you tick, so you can see what is still open.
What makes penetration testing lawful
The techniques are the same ones an intruder would use. However, written authorisation from the system owner is what separates the profession from the offence. So the scope and the authorisation always come first.
How to commission penetration testing well
Start with the business outcome you most need to protect. Then insist on a named principal, a fixed fee and a report written by the person who tested.
- One objective, stated in business terms
- A written scope signed by the system owner
- Hand-validated findings, not scanner output
- A retest once the fixes are applied
Where Sentinel Black fits
Full mandates run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Exposure Assessment starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. The method follows the Penetration Testing Execution Standard and the OWASP Web Security Testing Guide.
Questions on penetration testing in cyber security
Is penetration testing in cyber security the same as a scan?
No. A scan lists issues, while a test proves which of them an intruder could use.
How often is penetration testing in cyber security needed?
Usually yearly, and after major change such as a migration.
Does penetration testing replace an audit?
No. An audit checks controls exist, while a test checks they hold.
Who should own the result?
A named executive, so that fixes are funded and tracked.
Related guides
Request an introduction
Tell us what you need protected and what you are trying to prevent. A senior professional hacker reads every enquiry personally. Also, say who will receive the debrief, because a board briefing and an engineering briefing need different emphasis and detail. Replies come in writing, so the scope is on record.
Request an introduction